Bulk-loading files into SQL Server on Linux used to require a server-level sysadmin login. Microsoft has now made a narrower option generally available: the fixed bulkadmin server role and the ADMINISTER BULK OPERATIONS permission. Here is what changed, which versions include it, and what database and Linux administrators still need to configure.
What Microsoft announced
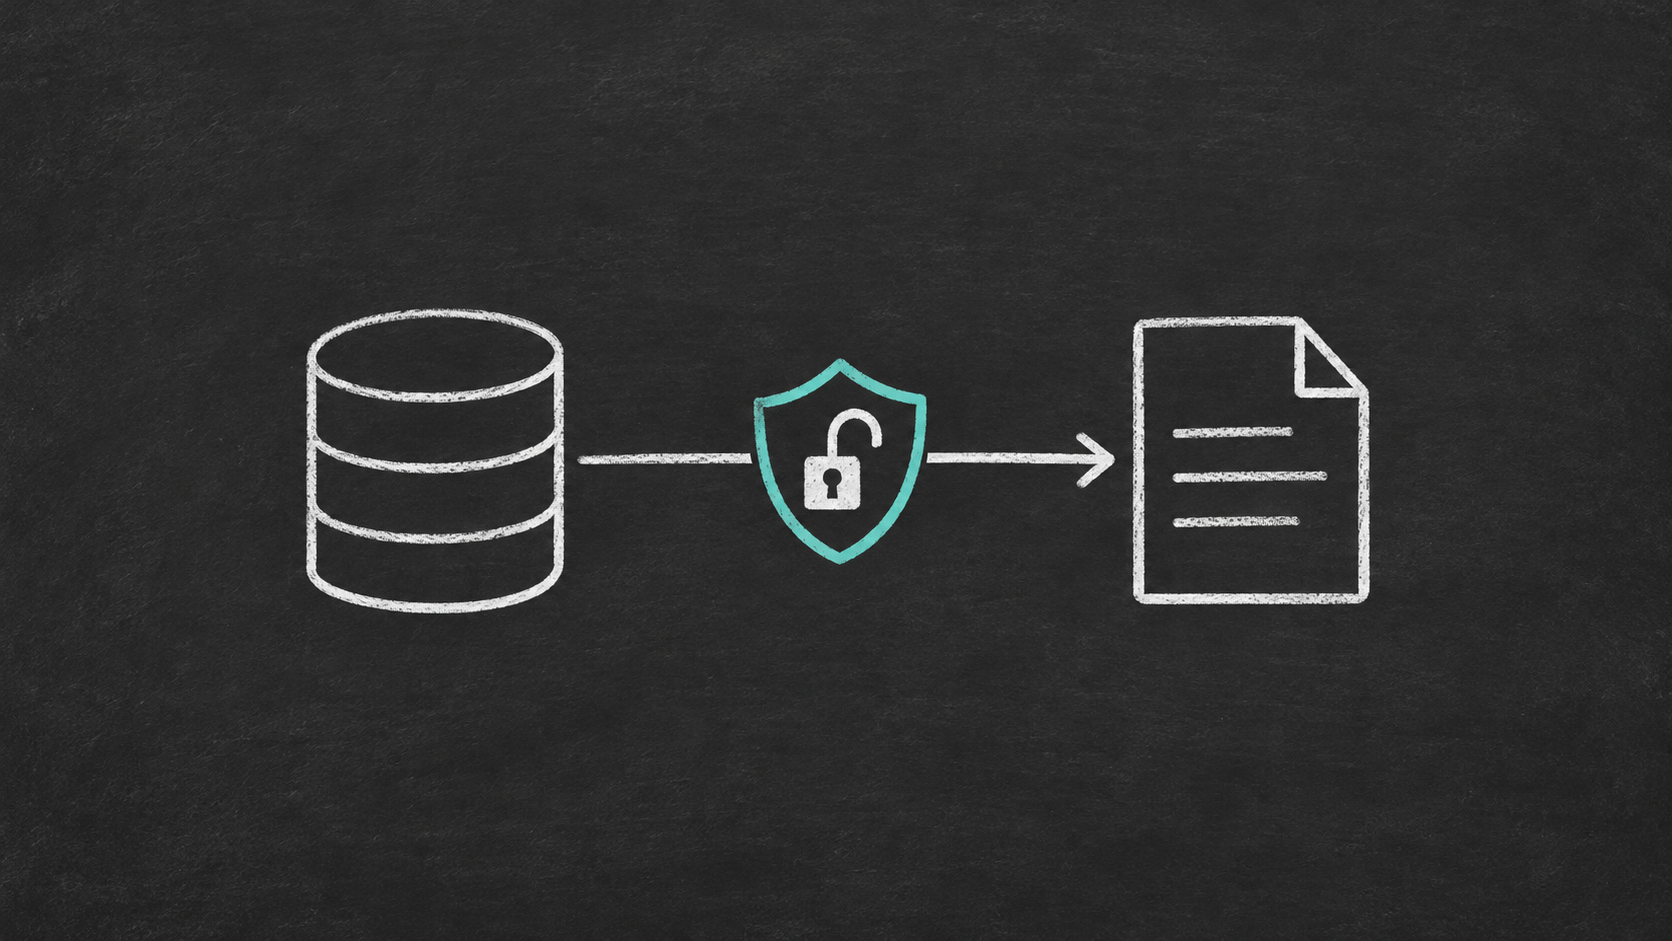
In its 1 October 2026 announcement, Microsoft said the feature is generally available in SQL Server 2025 CU9 and SQL Server 2022 CU27. It allows an appropriately permitted login to run BULK INSERT and OPENROWSET(BULK...) on SQL Server for Linux without granting sysadmin. The announcement covers Linux installations on premises, SQL Server on Azure VMs, and containers.
This is a permissions improvement for a specific operation. It does not make bulk import permissionless, and it does not grant the SQL Server service account access to files on the host.
SQL permission and Linux file access are separate
A working import depends on both SQL Server permissions and operating-system access:
- SQL Server: grant the login
bulkadminor the narrowerADMINISTER BULK OPERATIONSpermission, and grant the required permissions on the destination database objects. Microsoft’s BULK INSERT documentation describes the associated table permissions and options. - Linux: the SQL Server service account, normally
mssql, must be able to read the source file. The file path must also be permitted by the SQL Server bulk-operation configuration. See Microsoft’s bulk operations guide for SQL Server on Linux for the path and file-system requirements.
Keep the allowed path list as narrow as practical. A database permission cannot compensate for a missing Linux file permission, and granting broad access to directories creates unnecessary exposure.
Plan the upgrade and permission change
- Confirm the exact build. Check the installed cumulative update against Microsoft’s SQL Server 2025 build list or SQL Server 2022 build list. The GA versions in the announcement are CU9 and CU27 respectively.
- Choose the least-privilege grant. Decide whether the fixed
bulkadminrole or the individualADMINISTER BULK OPERATIONSpermission best matches your access model. Avoid usingsysadminjust to enable a file load. - Constrain file access. Configure only the required import directories, grant the service account the file-system access it needs, and avoid placing untrusted files in an approved directory.
- Test the full path. Run a representative import using the intended login and destination table. Test a rejected path and a login without the bulk permission too, so the security boundary is checked along with the successful case.
- Record ownership and monitoring. Document who places files, how long they remain available, who owns the import job, and how failures are surfaced.
When this matters
The change is useful where a Linux-hosted SQL Server imports files as part of a scheduled data pipeline and the old requirement for a sysadmin account was a barrier to a tighter security model. It does not replace a pipeline’s own validation, file handling, or audit controls. Keep those controls in place, particularly when files arrive from outside the database environment.
For teams using SharePoint data in a SQL reporting layer, the loading mechanism depends on the architecture: this announcement concerns file-based bulk operations in SQL Server, while our guide to monitoring SharePoint-to-SQL Server synchronisation after go-live covers freshness, failures, and downstream checks.
Sources
- Microsoft SQL Server Blog: BULKADMIN role support for SQL Server on Linux is now generally available
- Microsoft Learn: BULK INSERT (Transact-SQL)
- Microsoft Learn: Configure bulk import operations for SQL Server on Linux
- Microsoft Learn: SQL Server 2025 build versions and SQL Server 2022 build versions